In short: Rotterdam's refinery cluster concentrates people, hazardous processes and critical assets that must run safely around the clock. Key2XS gives operators governed, identity-linked control over physical keys — and the audit trail to prove CER compliance to authorities.
Keeping Rotterdam’s Refineries Safe with Key2XS and Proving CER Compliance
Rotterdam is Europe’s energy heartbeat. The port cluster hosts five major refineries and allied chemical sites an enormous concentration of people, assets, and hazardous processes that must run safely every hour of the year.
Over the last few years the risk picture has sharpened. Power disturbances in the area have shown how quickly operations can be impacted, while global incidents at oil & gas hubs underline the reality of hybrid (physical + cyber) threats.
Read more on the need of cyber resilience at the Port of Rotterdam here.
At the same time, Europe’s Directive on the Resilience of Critical Entities (CER, EU 2022/2557) is reshaping how critical operators must manage physical resilience, including insider risk and sabotage. Member States were required to transpose CER by 17 October 2024, with national regimes now rolling out; in the Netherlands, the Wet Weerbaarheid Kritieke Entiteiten (Wwke) and the Cyberbeveiligingswet (Cbw) were submitted to Parliament on 17 June 2025. Operators in scope should prepare now.
This article shows how Key2XS helps Rotterdam’s refineries enhance safety and demonstrably meet CER obligations by bridging digital identity (IAM) with electronic key systems to control, monitor, and audit all physical access.
Why keys are still your biggest blind spot
Even highly automated plants depend on mechanical and electronic keys for valves, cabinets, MCC rooms, substations, tank farm gates, rail racks, and vendor skids. In practice, risks concentrate around:
-
Standing privileges: long-lived keys that outlast jobs, shifts, or contracts.
-
Contractor access: dozens of service firms on site during turnarounds and brownfield works.
-
Distributed assets: remote pump stations, jetties, and pipe corridors far from the control room.
-
Audit gaps: incomplete, manual logs when authorities or insurers request evidence.
CER explicitly calls out resilience against natural hazards, sabotage, and insider threats areas where unmanaged keys become weak links.
What Key2XS does (in refinery terms)
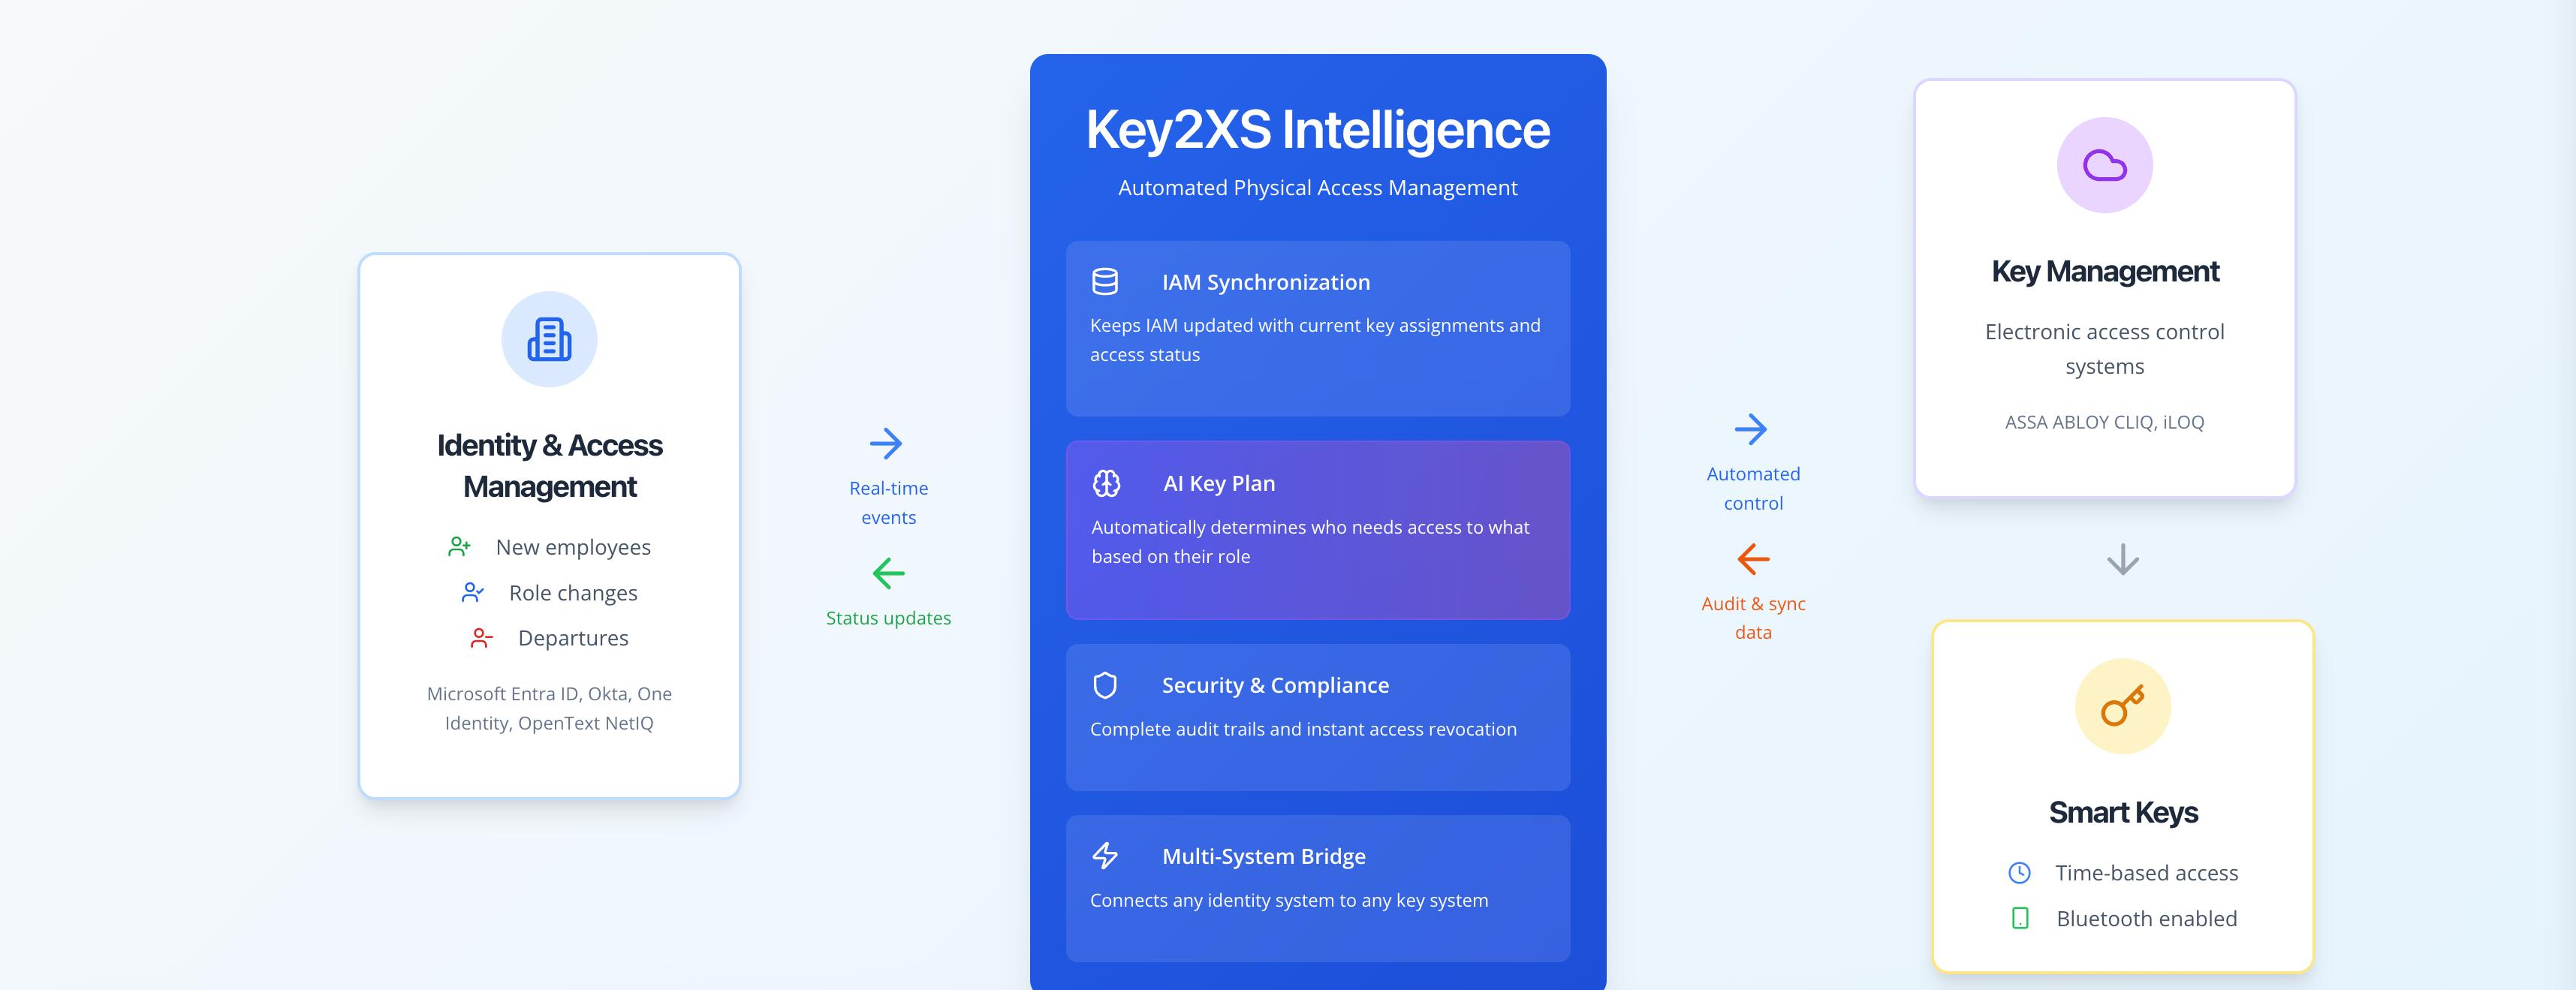
Key2XS connects your electronic key system (e.g., ASSA ABLOY CLIQ; iLOQ) to your Identity & Access Management (IAM) (e.g., Microsoft Entra ID, SailPoint, Okta, One Identity and others). The result is a single policy plane for both digital and physical access:
-
Role- & shift-based keys (JIT)
Keys are activated just-in-time for specific work orders, assets, and time windows, then auto-expire. No more standing privileges.
-
Permit-to-Work alignment
Only keys linked to an authorised job step (LOTO, hot work, confined space) can be activated; scope changes revoke access instantly.
-
Contractor onboarding/offboarding
Vendors are onboarded via IAM; no IAM identity = no key. Company exits or contract end dates revoke keys automatically.
-
Realtime visibility & audit
Every activation, use, and failed attempt is logged and streamed to SIEM/SOC. Auditors get tamper-evident trailsdown to cylinder level.
-
AI keyplan governance
Key2XS’ AI proposes least-privilege keyplans from roles, org charts, and uploaded infrastructure data; it flags SoD conflicts and over-provisioning.
-
Incident response
Lost key? Suspected insider? Remote kill deactivates keys and blocks affected zones. Access can be re-issued for emergency crews in minutes.
Mapping Key2XS to CER obligations
|
CER focus area |
What the Directive expects |
How Key2XS helps you evidence compliance |
|
Risk assessment & measures |
Identify critical operations; implement proportional resilience measures; address insider threats and sabotage. |
Replace standing privileges with JIT activation; enforce least-privilege keyplans; maintain end-to-end access telemetry for insider-risk analytics. |
|
Incident management |
Prevent, respond to, and recover from disruptions. |
One-click revocation; geo/asset scoping; auditable timelines for post-incident reports and insurer queries. |
|
Supply-chain resilience |
Manage dependencies and third parties safely. |
Contractor keys tied to IAM identities, PO/WO numbers, and time-boxed permits; automatic offboarding upon contract end. |
|
Reporting & oversight |
Demonstrate preparedness to the national competent authority. |
Exportable, time-stamped access logs and control attestations; metrics dashboards aligned to refinery KPIs. |
|
Coordination with cyber (NIS2) |
Align physical and cyber resilience. |
Stream physical-access events into SIEM/SOC; correlate with OT/IT alerts to spot hybrid attack patterns. |
(For background on CER scope, timelines, and national transposition, see the European Commission’s overview and enforcement updates, plus Dutch legislative status)
A refinery-ready rollout (90 days to value)
Weeks 0–2 – Foundations
-
Connect IAM (Entra/HRIS) and import refinery roles (operations, maintenance, turnaround, HSE).
-
Ingest asset registry (areas, units, cabinets, substations) and map cylinders/locks.
-
Define critical zones: crude & vacuum units, hydroprocessing, tank farms, jetties, substations, control rooms.
Weeks 3–6 – Pilot & JIT
-
Select one area (e.g., hydrocracker or a substation cluster) for pilot.
-
Turn on JIT keys for maintenance and emergency teams; integrate access telemetry into SIEM.
-
Align Permit-to-Work: only authorised tasks can trigger key activation
Weeks 7–10 – Scale & automate
-
Expand to contractors, scaffolders, NDT crews, and turnaround firms.
-
Enable AI keyplan and SoD checks; automatically flag excess or overlapping access.
Weeks 11–13 – Prove & optimise
-
Report KPIs: % JIT vs standing access, time-to-revoke, audit exceptions, MTTR for hybrid incidents, contractor onboarding time.
-
Prepare CER evidence pack: policies, process diagrams, sample logs, and monthly control attestations.
High-impact refinery use cases
-
Turnaround season control
Thousands of extra workers and dozens of vendors enter site gates. Key2XS issues time-boxed keys bound to work packages and revokes them when scopes close shrinking insider and theft exposure that rises during TARs. (Rotterdam’s recent large turnarounds show the vendor scale involved.)
-
Substation & jetty safety
OT alarms and grid events can coincide with physical access to high-energy zones. Key2XS correlates physical entry attempts with SIEM alerts to spot hybrid activity and prevent mis-operations. (A 2024 grid disturbance in the port illustrated how sensitive operations are to power anomalies.)
-
ARA-hub threat awareness
The Amsterdam–Rotterdam–Antwerp hub has seen security-relevant incidents in recent years; resilience is non-negotiable. Key2XS helps enforce least-privilege at the lock, not just the firewall.
What auditors and authorities will ask and how you answer
-
Who can open this cabinet/valve/room right now, and why?
→ Show the role-based entitlement and the active JIT grant bound to a job step.
-
How fast can you revoke all access for vendor X?
→ Immediate revocation via IAM; all keys for that vendor’s identities are deactivated and logged.
-
Prove no one had standing access to Unit 2 during hot work.
→ Export the access window ledger for Unit 2 and the task IDs; logs show failed attempts outside the window.
-
Demonstrate alignment with CER & Wwke.
→ Provide your policy mappings, resilience measures, SIEM correlation playbooks, and monthly control attestations.
Integration landscape (typical)
-
IAM / HR: Microsoft Entra ID, SailPoint, IdentityNow, Okta, One Identity, OpenText
-
Key systems: ASSA ABLOY CLIQ, iLOQ
-
OT/IT telemetry: Splunk, Microsoft Sentinel, Elastic, QRadar
-
Work management: SAP PM, Maximo, e-PTW
Key2XS sits in the middle, enforcing “no identity, no key”, turning every cylinder into a managed endpoint and every key into a revocable, auditable token.
Action checklist for Rotterdam refinery leaders
-
Identify critical zones and cylinders that must move to JIT access first.
-
Connect IAM and eliminate standing physical privileges in pilot areas.
-
Stream physical access logs to SOC and correlate with OT signals.
-
Align Permit-to-Work with key activation; block ad-hoc key issuance.
-
Produce a CER evidence pack and rehearse an insider-threat tabletop.
-
Extend to contractors and turnaround vendors before the next TAR.
Bottom line 
Recent incidents prove cyber resilience is not a luxury but a necessity.
Rotterdam’s refining cluster cannot afford blind spots between digital and physical security. Key2XS closes that gap shrinking attack surface, speeding incident response, and giving you the audit-ready trail that CER expects.