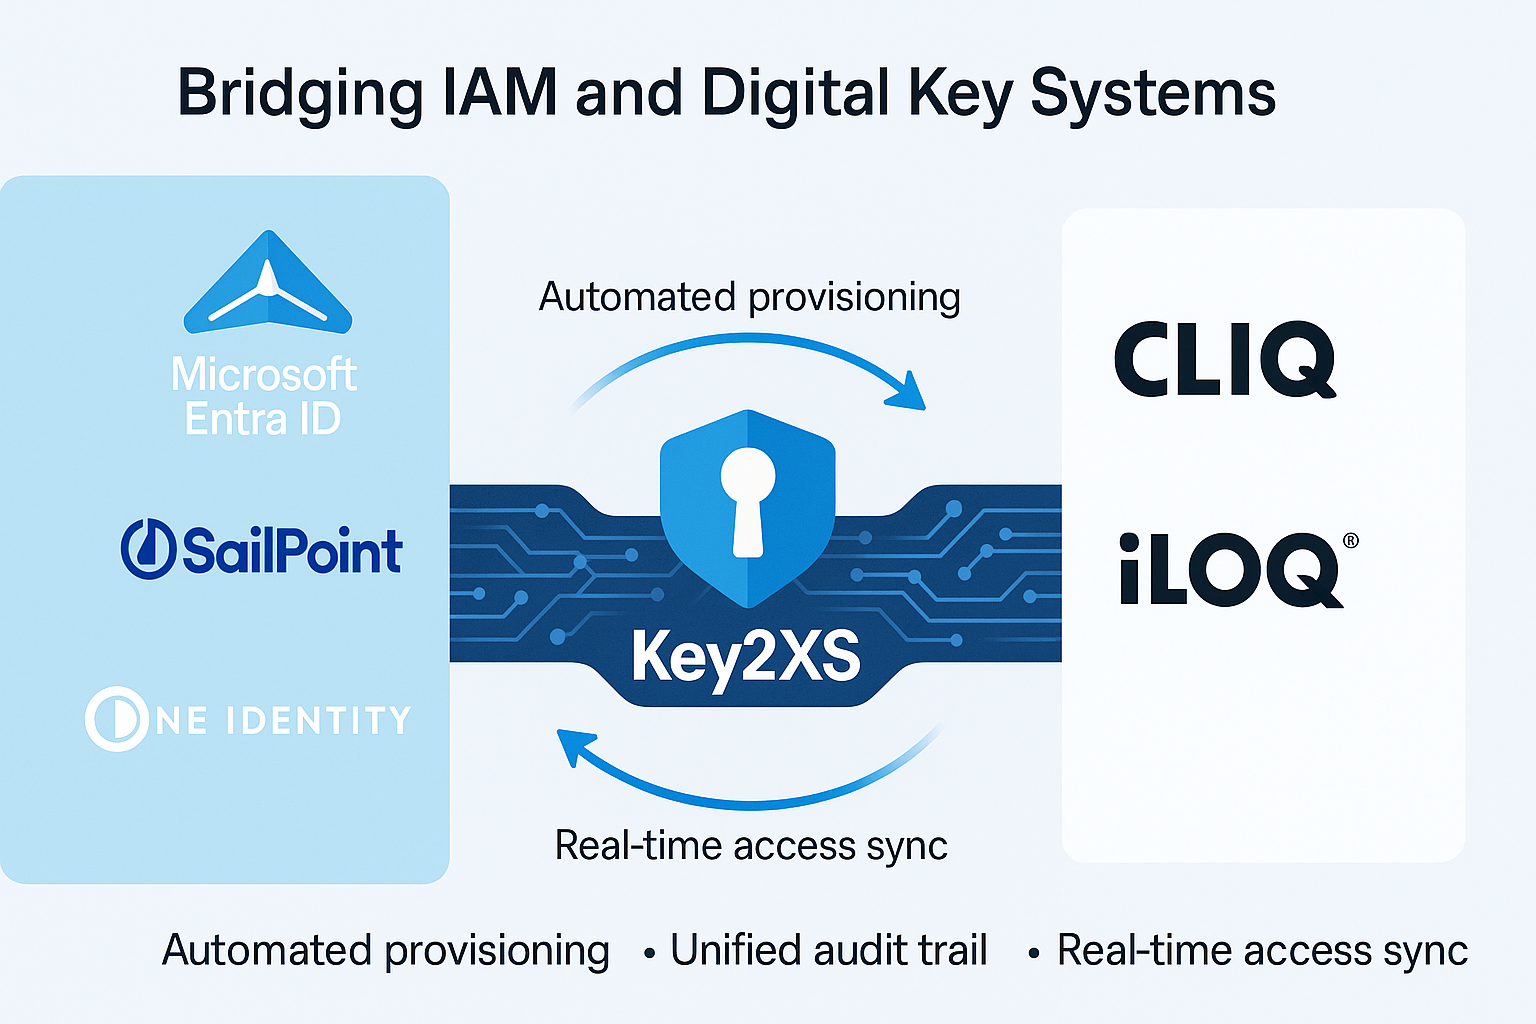
In short: Electronic key systems like ASSA ABLOY CLIQ and iLOQ often run isolated from both on-prem and SaaS identity platforms. Key2XS bridges that divide, so access rights stay consistent and auditable across IT, OT and cloud, regardless of where identities are managed.
Bridging the Gap: Solving On-Prem and SaaS-Managed Access Rights for Digital Keys
In today’s complex IT and OT environments, managing access rights across both on-premises systems and SaaS platforms is already a challenge. But when it comes to digital key systems, the complexity deepens. Many organizations rely on electronic key solutions—such as ASSA ABLOY CLIQ or iLOQ—to secure physical access to critical infrastructure. Yet, these systems often operate in silos, disconnected from modern Identity Governance & Administration (IGA) or Identity and Access Management (IAM) platforms.
This article explores how organizations can unify access control across on-prem and SaaS environments—including physical digital keys—into a single, compliant, and automated framework.
The Challenge: Disconnected Worlds
Traditional key management systems were designed before the cloud era. As a result:
-
Access rights for digital keys (e.g. issuing or revoking permissions) often require manual action.
-
These rights are typically managed in proprietary, on-prem applications—disconnected from cloud-based IAM solutions like Microsoft Entra ID, Okta, or SailPoint.
-
Lack of integration means delayed revocation of physical access when roles change or contracts end—posing a real security risk.
For organizations facing CER, NIS2, ISO 27001, or SOC2 compliance, this fragmentation introduces unnecessary audit complexity and operational overhead.
The Solution: Federated Access Control for Digital Keys
To bridge the gap, leading organizations are adopting a federated model that integrates digital key systems with their existing IAM/IGA infrastructure. Here’s how it works:
1. Central Identity as Source of Truth
All users—internal and external—are managed through the central IAM platform. Role-based access control (RBAC) and entitlements are defined in a SaaS or hybrid IAM solution.
2. Real-Time Key Provisioning
Using a middleware or integration platform (like Key2XS), the system automatically provisions or revokes digital key access based on IAM role changes, identity lifecycle events, or policy triggers.
3. Unified Audit Trail
All actions—digital key issuance, activation, access logs—are synchronized with the organization’s audit system, allowing for real-time monitoring and compliance reporting.
4. Policy-Driven Access Governance
IGA systems (e.g. SailPoint, One Identity) enforce periodic access reviews for both IT and OT access rights, ensuring that no dormant or orphaned key access exists.
Use Case: Hybrid Utility Company
A Dutch utility managing 10,000 substations implemented an IAM-integrated digital key system using Key2XS. By linking Microsoft Entra ID with their ASSA ABLOY CLIQ system:
-
Access rights are updated in near-real time when a technician changes teams or leaves the organization.
-
Facility managers no longer need to track physical keys manually.
-
CER and NIS2 audit reporting includes both digital and physical access controls in one dashboard.
Key Benefits
- Eliminate manual processes for digital key management
- Accelerate provisioning and revocation of physical access
- Achieve compliance with CER, NIS2, ISO, and internal governance policies
- Unify IT and OT access control into a single pane of glass
- Support zero trust principles—even for physical assets
Final Thoughts
The convergence of physical and digital access rights is no longer a futuristic ideal—it’s a regulatory and operational necessity. By integrating digital key systems with IAM and IGA platforms, organizations can automate, audit, and secure access across the board—no matter where it’s hosted.
Want to see how this works in practice?
Explore how Key2XS connects physical key systems like CLIQ to Microsoft Entra ID, SailPoint, and One Identity—bridging on-prem and cloud access management with AI-powered automation.